Autonomous Threat Defense Across Endpoints, Cloud & Identity
Modern enterprise security can no longer rely on fragmented alerts and manual correlation. SentinelOne Singularity™ XDR unifies telemetry across endpoints, cloud workloads, and identity providers into one autonomous behavioral AI engine — detecting unknown zero-days in milliseconds and reversing ransomware damage with 1-Click Rollback.
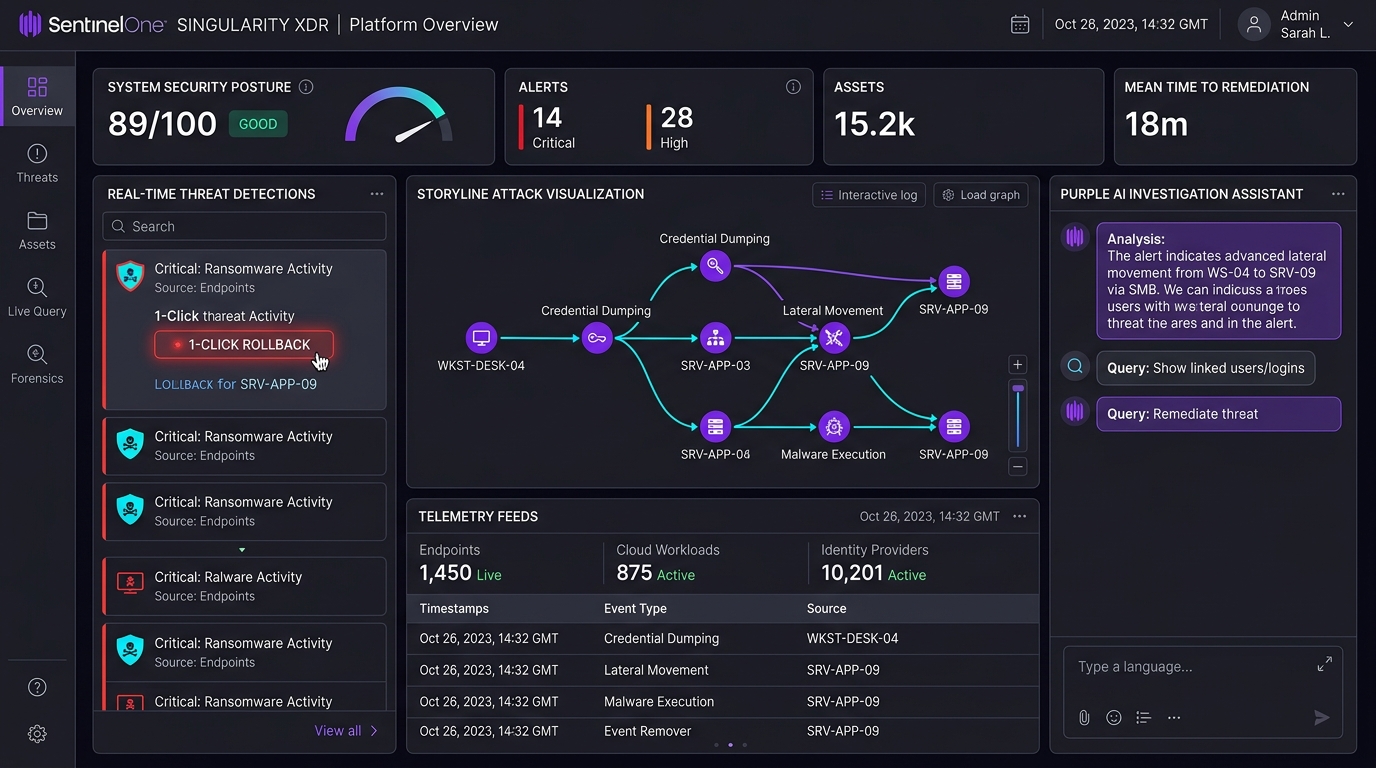
- 1-Click True Rollback
- Storyline™ Kernel Telemetry
- Purple AI GenAI Assistant
- Zero-Delay Real-Time Defense
- Autonomous CWPP & CSPM
- ITDR Active Directory Defense
- Unified Singularity Data Lake
Six Pillars of the Singularity™ Platform
SentinelOne replaces fragmented point security products with a unified, autonomous XDR platform engineered to protect every endpoint, cloud workload, identity, and data stream.
Singularity™ Endpoint (EDR/EPP)
Autonomous on-agent behavioral AI prevents, detects, and neutralizes malware, fileless scripts, zero-days, and live ransomware across Windows, macOS, and Linux without requiring cloud connectivity.
- Storyline™ tracks all OS process execution chains
- 1-Click Rollback reverses ransomware encryption
- Device Control & Network Quarantine in 1 click
Singularity™ Cloud Security (CWPP/CSPM)
Real-time runtime protection for Linux VMs, Docker containers, and Kubernetes clusters in AWS, Azure, and GCP, coupled with agentless Cloud Security Posture Management.
- Real-time kernel-level eBPF container telemetry
- Agentless CSPM, CIEM & IaC misconfiguration audits
- Automated kill & quarantine of rogue cloud processes
Singularity™ Identity (ITDR)
Identity Threat Detection and Response (ITDR) protects Active Directory, Microsoft Entra ID, and Okta from credential dumping, Kerberoasting, privilege escalation, and lateral movement.
- Intercepts Mimikatz and LSASS memory dumping
- Injects deceptive decoys and fake credentials
- Continuous AD hygiene and shadow admin discovery
Purple AI Autonomous Analyst
An embedded, agentic generative AI security analyst that translates natural language questions into complex threat queries, summarizes attack timelines, and recommends remediation steps.
- 80% reduction in investigation and triage time
- Converts plain English prompts into deep PowerQueries
- Automated executive incident summary generation
Singularity™ Data Lake & STAR
Petabyte-scale, hyper-fast security data lake that ingests, normalizes, and retains high-fidelity telemetry across your entire IT stack with Storyline Active Response (STAR) automated detection rules.
- Sub-second query response on billions of events
- Custom STAR automation rules to contain threats
- OCSF standard data schema compatibility
Vigilance Respond (24x7 MDR)
Augment your internal security team with 24/7/365 managed threat hunting, triage, and rapid incident containment executed by elite SentinelOne SOC analysts backed by guaranteed SLAs.
- 24x7 continuous monitoring and active threat hunting
- Direct analyst consultation on critical incidents
- Zero alert fatigue for your internal security team
How Storyline™ Resolves Attacks in Seconds
Unlike legacy EDR that generates thousands of disconnected log entries, SentinelOne’s Storyline™ tracks every OS relationship, thread, file modification, and network connection as one contextualized story.
Kernel Telemetry
Continuous on-agent monitoring of all OS processes, DLL loads, and registry changes in real time.
Behavioral AI
Static & dynamic AI heuristics evaluate malicious execution without relying on signatures.
Storyline Graph
Disparate events are stitched together into a complete root-cause attack timeline automatically.
Auto Containment
Malicious processes are terminated, host isolated, and lateral movement channels instantly blocked.
1-Click Rollback
Encrypted files are restored via shadow copy snapshots, returning the device to its pre-attack state.
One Unified Data Lake Across Your Entire Estate
Break down security silos. Singularity XDR normalizes telemetry across your existing technology investments — from firewalls and identity providers to cloud infrastructure and SaaS apps.
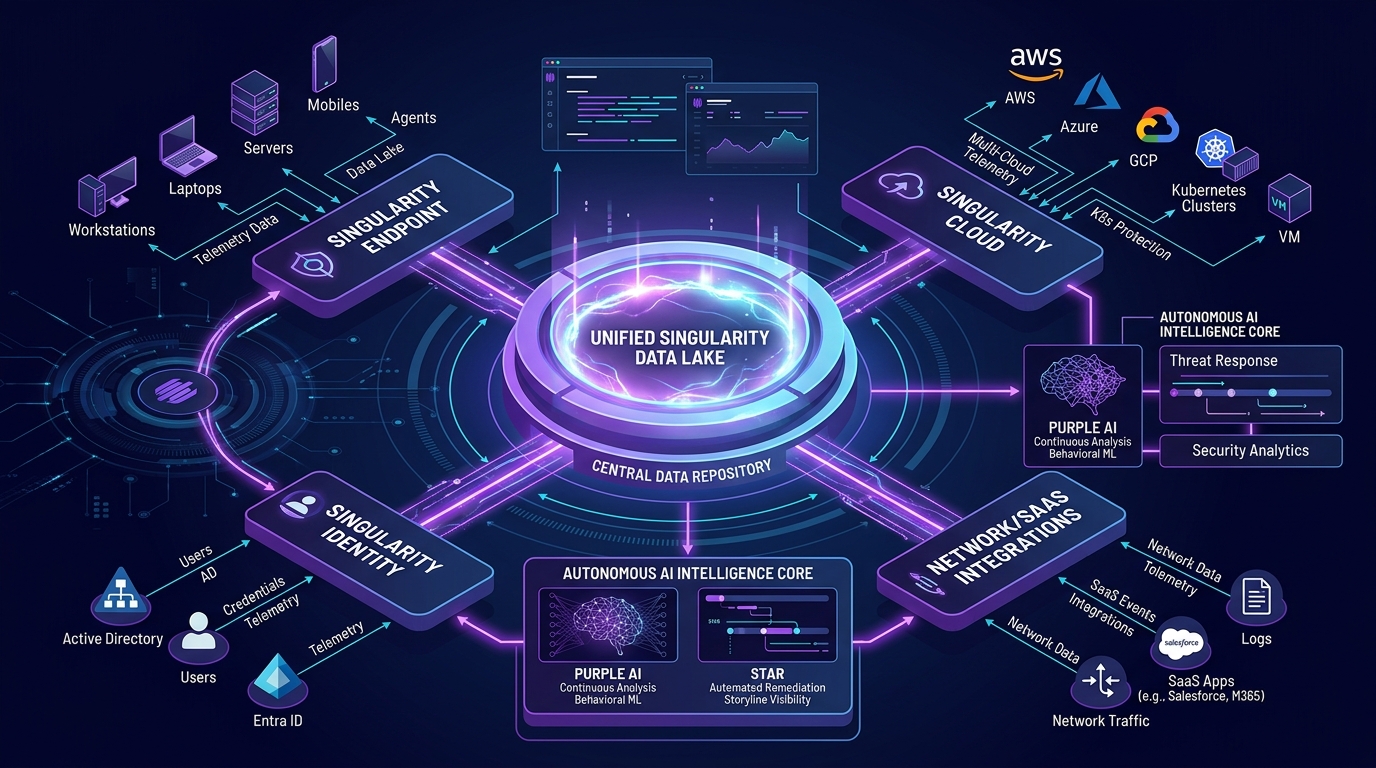
Multi-Source Ingestion & Normalization
Consolidate logs from AWS, Azure, GCP, Okta, Cisco, Palo Alto Networks, Microsoft 365, and Salesforce into an OCSF-compliant data lake.
Storyline Active Response (STAR)
Turn threat intelligence into action by deploying automated custom rules that trigger machine-speed containment policies across endpoints and networks.
Purple AI Natural Language Hunting
Empower SOC analysts of all experience levels to conduct complex threat hunts, parse IoCs, and generate incident reports via intuitive conversational queries.
100+ Singularity Marketplace Integrations
Pre-built, no-code integrations allow bidirectional security workflows with your existing SIEM, SOAR, IT ticketing, and communication stacks.
Legacy EDR / SIEM vs. Autonomous Singularity XDR
Compare how SentinelOne’s behavioral AI architecture outperforms legacy signature-based endpoint tools and labor-intensive manual SIEM correlation.
| Security Capability | Traditional EDR / Legacy Antivirus | SentinelOne Singularity™ XDR |
|---|---|---|
| Threat Detection Model | Reactive signatures & cloud lookups | On-agent behavioral AI & heuristic ML |
| Offline Endpoint Protection | Degraded when disconnected from cloud | 100% Autonomous on-agent prevention |
| Ransomware Recovery | Manual disk wipe & backup restoration | 1-Click True Rollback to pre-attack state |
| Alert Correlation | Thousands of noisy, disconnected alerts | Storyline™ stitches execution into 1 story |
| Generative AI Assistance | Basic query builders or none | Purple AI natural language security analyst |
| MITRE ATT&CK Evaluations | High configuration changes & delays | 100% Protection, 100% Detection, 0 Delays |
| Cross-Surface Coverage | Separate consoles for endpoint, cloud, AD | Single console for Endpoint, Cloud & Identity |
In-Depth Guides to Autonomous Cyber Defense
Explore expert white papers on architecting zero-trust endpoint security, evaluating MITRE ATT&CK results, and accelerating SOC response times.
No White Papers available at the moment. Please check back later.
See Singularity XDR in Action
Watch live demonstrations of SentinelOne stopping ransomware attacks, executing 1-Click Rollback, and triaging complex threats with Purple AI.
Parsing 7: Structured Data part 2
Parsing 6: Structured Data part 1
Parsing 5: Attributes and Rewrites
Parsing 4: Patterns and Groupers
Parsing 3: Formats
Parsing 2: Regex
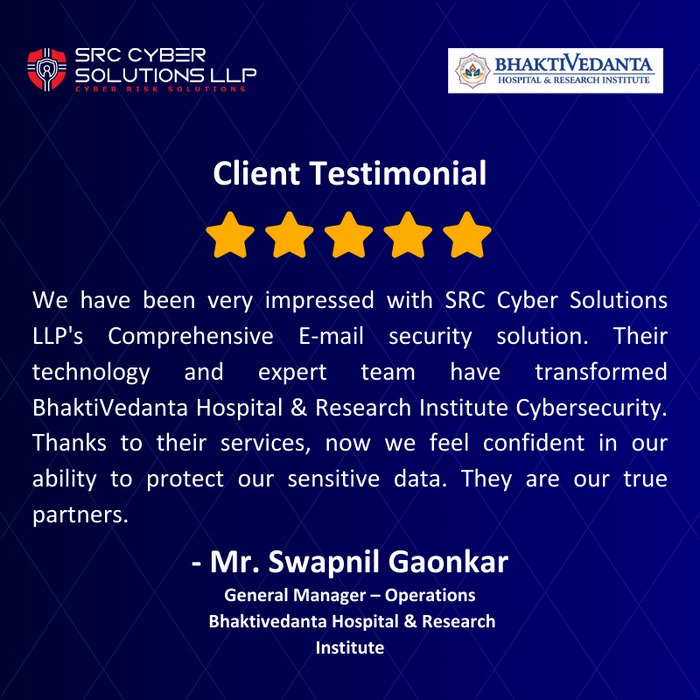
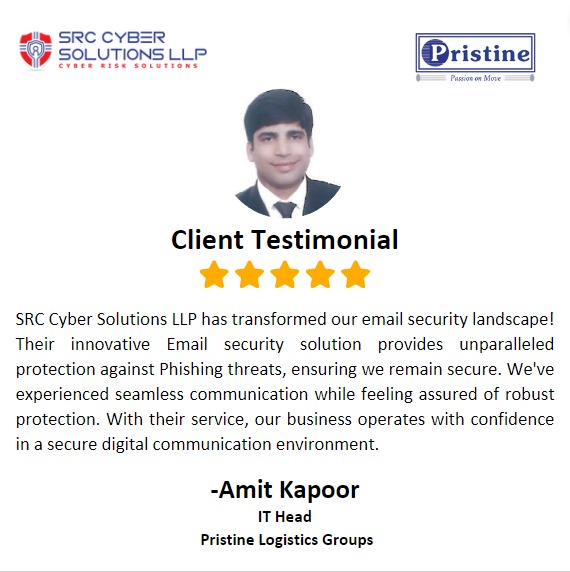
Client Endorsements
What Industry Leaders Say About Our Solutions


Ready to Experience Autonomous Threat Defense?
Schedule a personalized demonstration with SRC Cyber Solutions LLP. We’ll show you how SentinelOne Singularity™ XDR detects unknown threats, visualizes Storyline™ root causes, and restores encrypted files in seconds.
Latest Research & Security Advisories
Stay ahead of emerging adversary tradecraft, ransomware developments, and SOC modernization best practices.
No blogs available at the moment. Please check back later.
Office Location
MR-01, Statesman House, 5th Floor,
148, Barakhamba Road, Connaught Place,
New Delhi - 110001
Phone
Contact Us
Reach out to our cybersecurity specialists for customized solutions & live demos.
Explore Our Comprehensive Solutions
Dive into our diverse range of enterprise security services designed to protect your organization at every layer.
Comprehensive Email Security
Guard against sophisticated email threats with our AI-powered protection system. From phishing attempts to business email compromise, our solution detects and neutralizes...
Explore SolutionAsset Visibility And Risk Management
Build a stronger security culture through comprehensive cyber security training programs. Our hands-on approach ensures your team understands modern cyber threats and...
Explore SolutionThird Party Data Flow Security
Protect your organization from data flow management risks with advanced monitoring and control. Our platform provides complete visibility and protection for third-party...
Explore SolutionAgentless Micro-Segmentation
Implement automated microsegmentation without complex agent deployments. Create secure zones in your network to contain and control potential threats. Protect critical assets...
Explore SolutionCloud-Native Application Protection Platform
Protect cloud workloads, Kubernetes, containers, and multi-cloud environments with a unified Cloud-Native Application Protection Platform (CNAPP).
Explore Solution
FAQ
FAQs: Singularity XDR
What problem does the Singularity XDR solution solve?
It closes the operational gap most teams have in extended detection and response (XDR) - replacing manual scripts, spreadsheets, or ad hoc review with a structured, continuously running solution.
How does the Singularity XDR solution work?
In short: correlating signals from endpoints, cloud workloads, and identity systems into one view, so a threat that touches multiple systems is caught as one incident instead of several disconnected alerts. The solution automates that work end to end and routes anything that needs a human decision to your team.
What does implementation typically involve?
Implementation starts with a scoping review of your current environment, followed by phased deployment so security teams needing unified threat detection across endpoints, cloud, and identity aren't disrupted mid-rollout. Timelines depend on environment size and complexity.
Is the Singularity XDR solution suitable for a hybrid or multi-site organization?
Yes - it's designed to give one consistent view across distributed sites and hybrid environments rather than requiring a separate setup per location.
Can we read the full solution brief?
Yes - a downloadable solution brief covering scope, approach, and outcomes is available on this page.