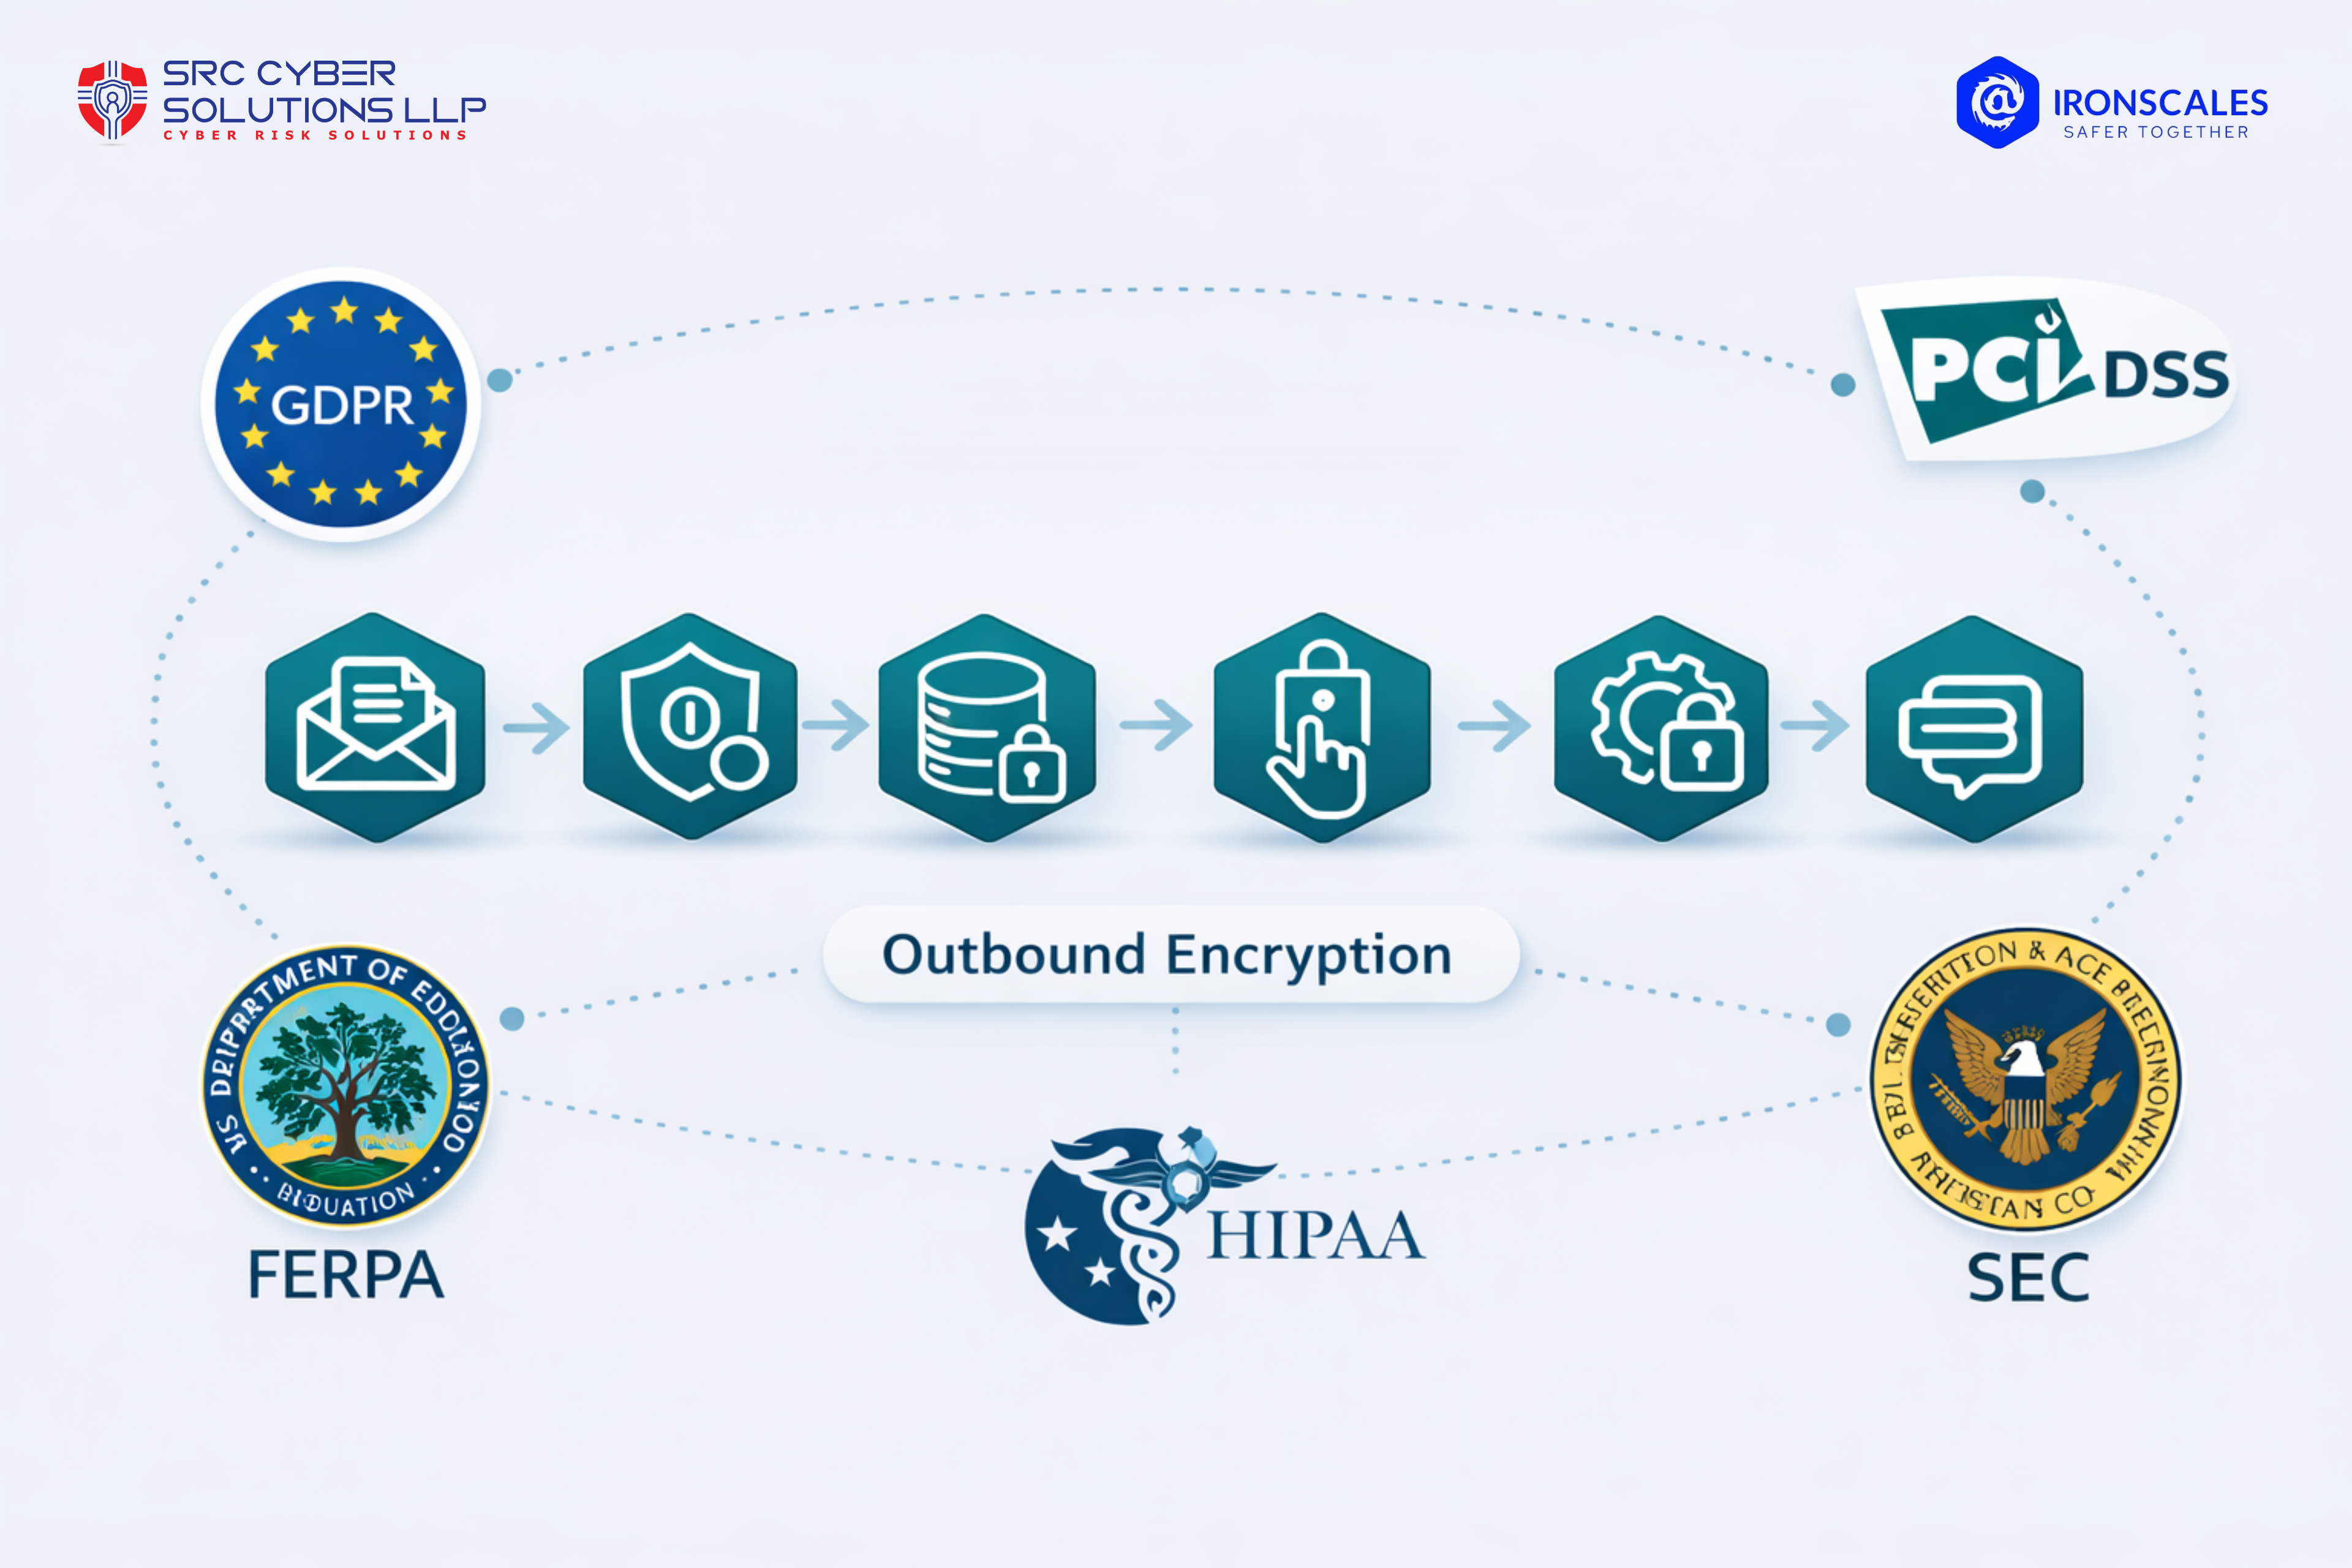
The Compliance Cliff: Email Encryption and Data Security Unpacked
Explore the need for outbound email encryption to enhance data security and compliance, addressing increasing regulatory pressures and adoption challenges.
Discover how our solutions have empowered organizations to overcome challenges, achieve operational excellence, and drive transformative growth. Learn from real-world success stories.
Explore the need for outbound email encryption to enhance data security and compliance, addressing increasing regulatory pressures and adoption challenges.
Anthropic's leaked Claude Mythos model is "far ahead" in cyber capabilities. Here's why it signals a new era of AI-powered phishing and what defenders must do now.
Discover why traditional SEGs are failing MSPs and how modern ICES solutions can bridge the gap for better client protection and operational efficiency.
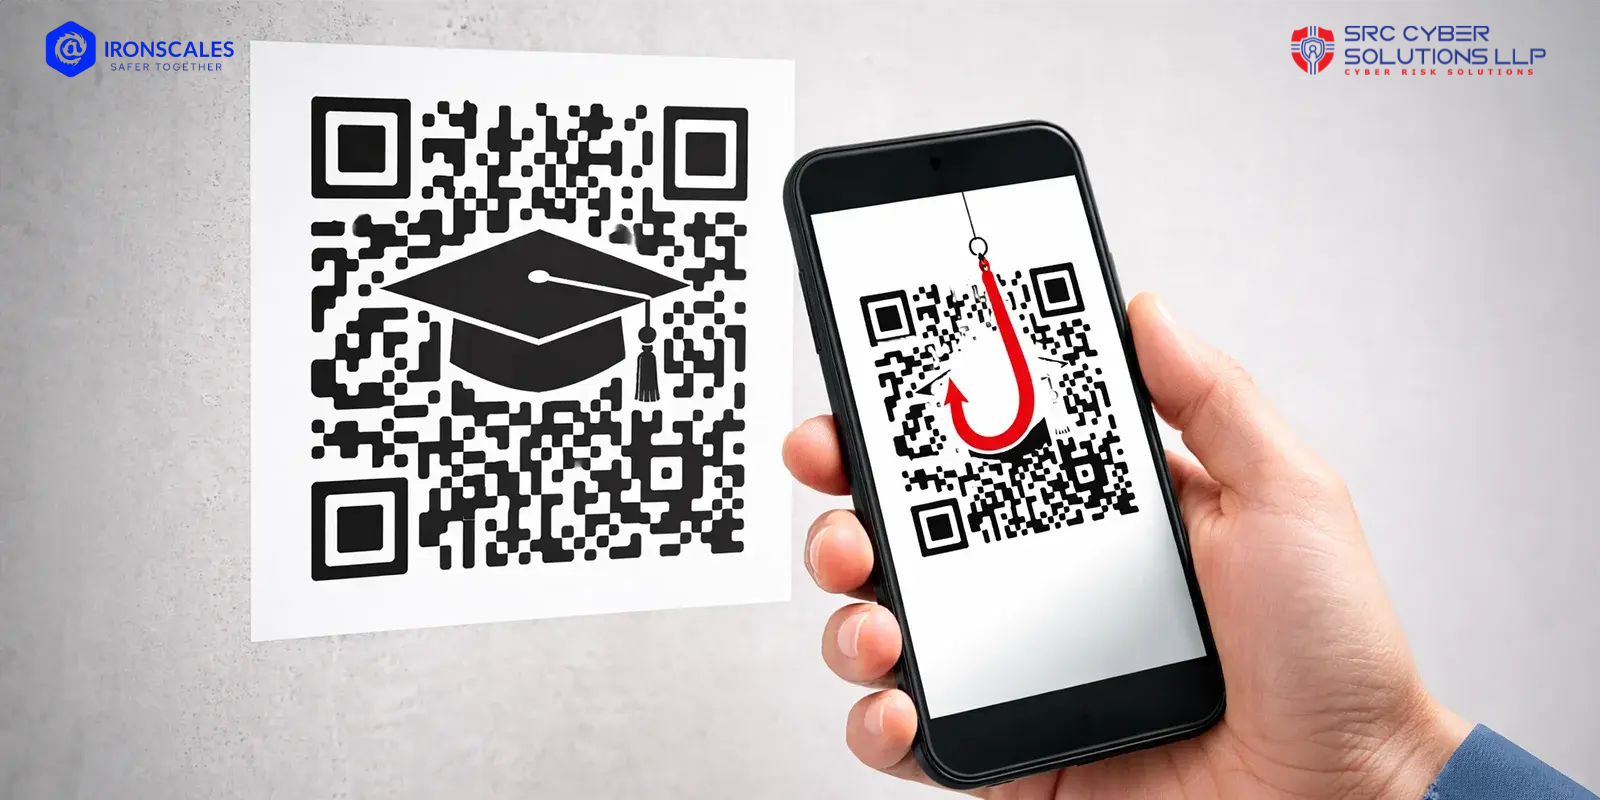
QR codes are everywhere in schools—and so are the phishing attacks hiding inside them. 15,000+ malicious QR codes target education daily. Here's why.
MSPs must shift QBRs from operational reviews to risk-focused discussions, aligning with client-specific compliance and security needs for 2026
ATOs are the new BEC. We're seeing it on our end and other companies have certainly taken notice. Attackers compromised 6.2 million customer accounts across 1,027 large organizations in 2024 according to Kasada’s 2025 Account Takeover Attack Trends Report, underscoring how routine ATO incidents have become for enterprise brands.
Email security is the set of defenses - filtering, authentication, and behavioral analysis - that stop phishing, malware, and business email compromise (BEC) before they reach an inbox.
As IT environments grow more distributed and threats more automated, gaps in email security are exactly what attackers look for first - making it one of the higher-leverage areas to get right.
The most common pattern is treating email security as a one-time setup rather than an ongoing program - controls drift out of date as the environment changes, and nobody notices until something goes wrong.
Continuously, ideally - email security works best as an always-on program rather than a quarterly or annual checklist item, since new risks appear between review cycles too.
This blog is updated regularly with practical articles on email security and related topics - browse the full archive on this page.