Across India, EMEA and APAC GCCs, the security teams we work with describe the same problem. Their environments now span public cloud, private data centres, Kubernetes clusters and a distributed workforce on laptops. Each of those layers usually came with its own tool, its own console and its own alert queue.
The result is plenty of data but little clarity. Analysts spend their time switching screens and stitching evidence together by hand, or spending AI tokens with different data sets, while paying for the connectors and the need to verify the AI outputs, which are Blackbox to SOC teams.
while the risks that matter wait in the backlog. Attackers, meanwhile, move freely between endpoints and cloud accounts.
That is why SRC Cyber Solutions works with Uptycs. Uptycs gives security teams one place to see their attack surface, understand which risks matter most, and act on them quickly.
One platform, one data model
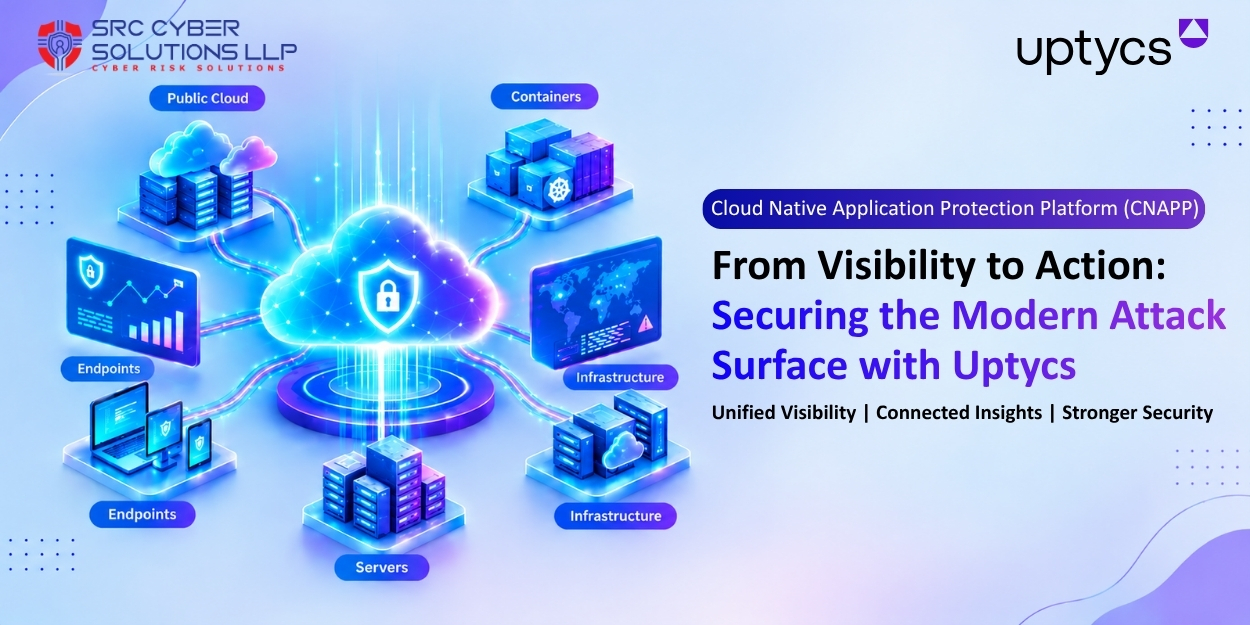
Uptycs is a unified cloud and workload security platform. It collects security telemetry from cloud accounts, containers and Kubernetes, Linux and Windows servers, and macOS and Windows endpoints. That data is normalized close to where it is collected, then streamed into a single security data lake.
Because everything shares one data model, teams can follow an attack as it crosses from a laptop into a cloud workload, without exporting logs between tools. The same platform covers capabilities that are often bought separately:
-
Cloud security posture (CSPM, KSPM): find misconfigurations across cloud accounts and Kubernetes.
-
Identity and entitlements (CIEM): spot over-privileged users, roles and service accounts.
-
Workload protection (CWPP): agentless scanning to get coverage fast, plus runtime protection where it matters most.
-
Detection and response (CDR, XDR): detects threats across cloud, servers and endpoints, and investigate them in one place.
-
Vulnerability management: see vulnerable packages and images across the estate, in context.
For analysts, this means one console and one query language for investigations, including searches across historical data, rather than a separate workflow for each tool.
Prioritizing the risks that matter
Most teams do not lack findings. They lack a way to decide which ten findings to fix this week. Uptycs supports a continuous threat exposure management (CTEM) approach: it connects vulnerabilities, misconfigurations, identity risks and live threat activity on the same asset, so teams can see which exposures are reachable and exploitable.
That context changes the conversation. A critical CVE on an isolated test server and the same CVE on an internet-facing workload with an over-privileged role are not equal risks. Uptycs helps teams see the difference, understand the potential blast radius, and route the right fix to the right owner.
A Risk – which comprises of alerts, detections, misconfigurations, config drift, vulnerability and compliance issue of a cloud resource or a workload its all in one place, with prioritization appended with Uptycs scoring.
The practical difference
|
CVSS |
Uptycs Score |
|
|---|---|---|
|
Scope |
Vulnerability in isolation |
Vulnerability + your environment |
|
Changes over time? |
Base score doesn't; Temporal/Environmental can but rarely used |
Yes, dynamically as context changes |
|
Answers |
"How bad could this be?" |
"How bad is this, here, right now?" |
|
Use case |
Standardized comms, compliance |
Actual remediation triage/prioritization |
Juno AI: an analyst you can verify
Skilled security analysts are scarce in every market we serve. Juno AI, built into the Uptycs platform, works alongside them. It interprets detections, correlates related signals and helps analysts’ triage and investigate incidents faster.
What sets Juno apart is that its conclusions are verifiable. Its insights are grounded in the telemetry in your own environment, so analysts can check the evidence behind an answer instead of taking it on trust. For lean teams, that means less time on routine triage and more time on the incidents that need human judgement.
Making compliance continuous
Regulators in our region are raising the bar, and audits increasingly expect evidence of continuous monitoring rather than a point-in-time snapshot. Uptycs continuously checks cloud accounts, servers and endpoints against security benchmarks and compliance frameworks, flags drift as it happens, and gives teams the evidence auditors ask for.
, e.g. CIS Benchmarks, PCI DSS, ISO 27001, SOC 2, NIST, and any regional frameworks relevant to SRC's customers.
Why SRC Cyber Solutions partners with Uptycs
We chose Uptycs because it fits how our customers run their environments: hybrid, multi-cloud and growing faster than their security teams. Instead of adding another point product, customers can consolidate several tools onto one platform and one data model.
As Uptycs' partner in India, the GCC, Africa and APAC, SRC provides local presales support, proof-of-value deployments and onboarding, so customers see results in their own environment before they commit.
See Uptycs in your environment. Book a demo with SRC Cyber Solutions
About SRC Cyber Solutions LLP
SRC Cyber Solutions LLP is a renowned name in India for Cybersecurity. We are known for our exclusive distribution of cutting -edge solutions in India, GCC, Africa and APAC. We take pride in offering a comprehensive suite of Cybersecurity solutions which includes Platforms and Technologies for Al-powered Comprehensive Email Security, Automated Patch and Endpoint Management, Zero Trust Hardware Access, securing the Cloud environments with Hybrid Cloud Workload Protection, enhancing Network Security with Agentless Micro - Segmentation, ensuring Third-Party Data Flow Management and API Management, and Agentless Compliance Management, thereby strengthening our commitment to protecting organizations against evolving known and unknown Cyber Threats. With a focus on embracing innovation, we continuously evolve to meet the dynamic threat landscape, offering a comprehensive range of Nex-Gen technologies with a high degree of automation, reducing the dependency on IT Resources and ensuring a strong value proposition.
About Uptycs
Uptycs is the leading cloud security platform for large hybrid cloud environments. We protect workloads wherever they run, while extending security visibility from development to runtime. That’s why enterprises like PayPal, Comcast, and Nutanix rely on Uptycs to secure their mission-critical workloads. First-generation CNAPP solutions don’t have all the data needed to manage and prioritize risk. With Uptycs, data is power! We have no trouble giving you deeper context so you can focus on what truly matters. Most CNAPPs can tell you if a vulnerable workload is exposed to the internet, but can they show you vulnerable packages running now, or three weeks ago, and if and how you were breached? Uptycs can. Uptycs brings teams together to optimize security operations, ensure compliance, and accelerate remediation across cloud workloads, containers, Kubernetes, and software pipelines – all from a single security console, policy framework, and data lake. Shift up your cybersecurity with Uptycs. Learn more at uptycs.com.
Frequently Asked Questions
What is Uptycs Cloud Security?
Uptycs is a cloud and workload security platform that helps organizations monitor cloud environments, Kubernetes, servers and endpoints from a unified console. It combines security telemetry to help teams detect threats, identify vulnerabilities and prioritize risks.
How does Uptycs help organizations secure their attack surface?
Uptycs helps organizations identify vulnerabilities, cloud misconfigurations, excessive permissions and suspicious activity across their environments. By connecting these findings with asset and threat context, security teams can prioritize exposures and focus remediation efforts on the risks that matter most.
What is the difference between CVSS and Uptycs Risk Scoring?
CVSS provides a standardized assessment of vulnerability severity, while Uptycs risk scoring adds environmental context to help teams evaluate the significance of exposures in their own infrastructure. This context can support more effective vulnerability prioritization and remediation planning.
How does AI help security teams investigate threats in Uptycs?
Uptycs Juno AI assists security analysts with interpreting detections, correlating related security signals and investigating incidents. By grounding its insights in available environmental telemetry, it can help analysts validate findings and reduce manual investigation effort.
How can SRC Cyber Solutions help businesses implement Uptycs?
SRC Cyber Solutions supports organizations across India, the GCC, Africa and APAC with Uptycs presales guidance, proof-of-value deployments and onboarding. Businesses can evaluate how the platform fits their hybrid cloud security requirements and operational workflows.